

Creating an Organization and Becoming Organization Admin
- Sign up or create a new organization in Condense Console https://console.condense.zeliot.in/signUp
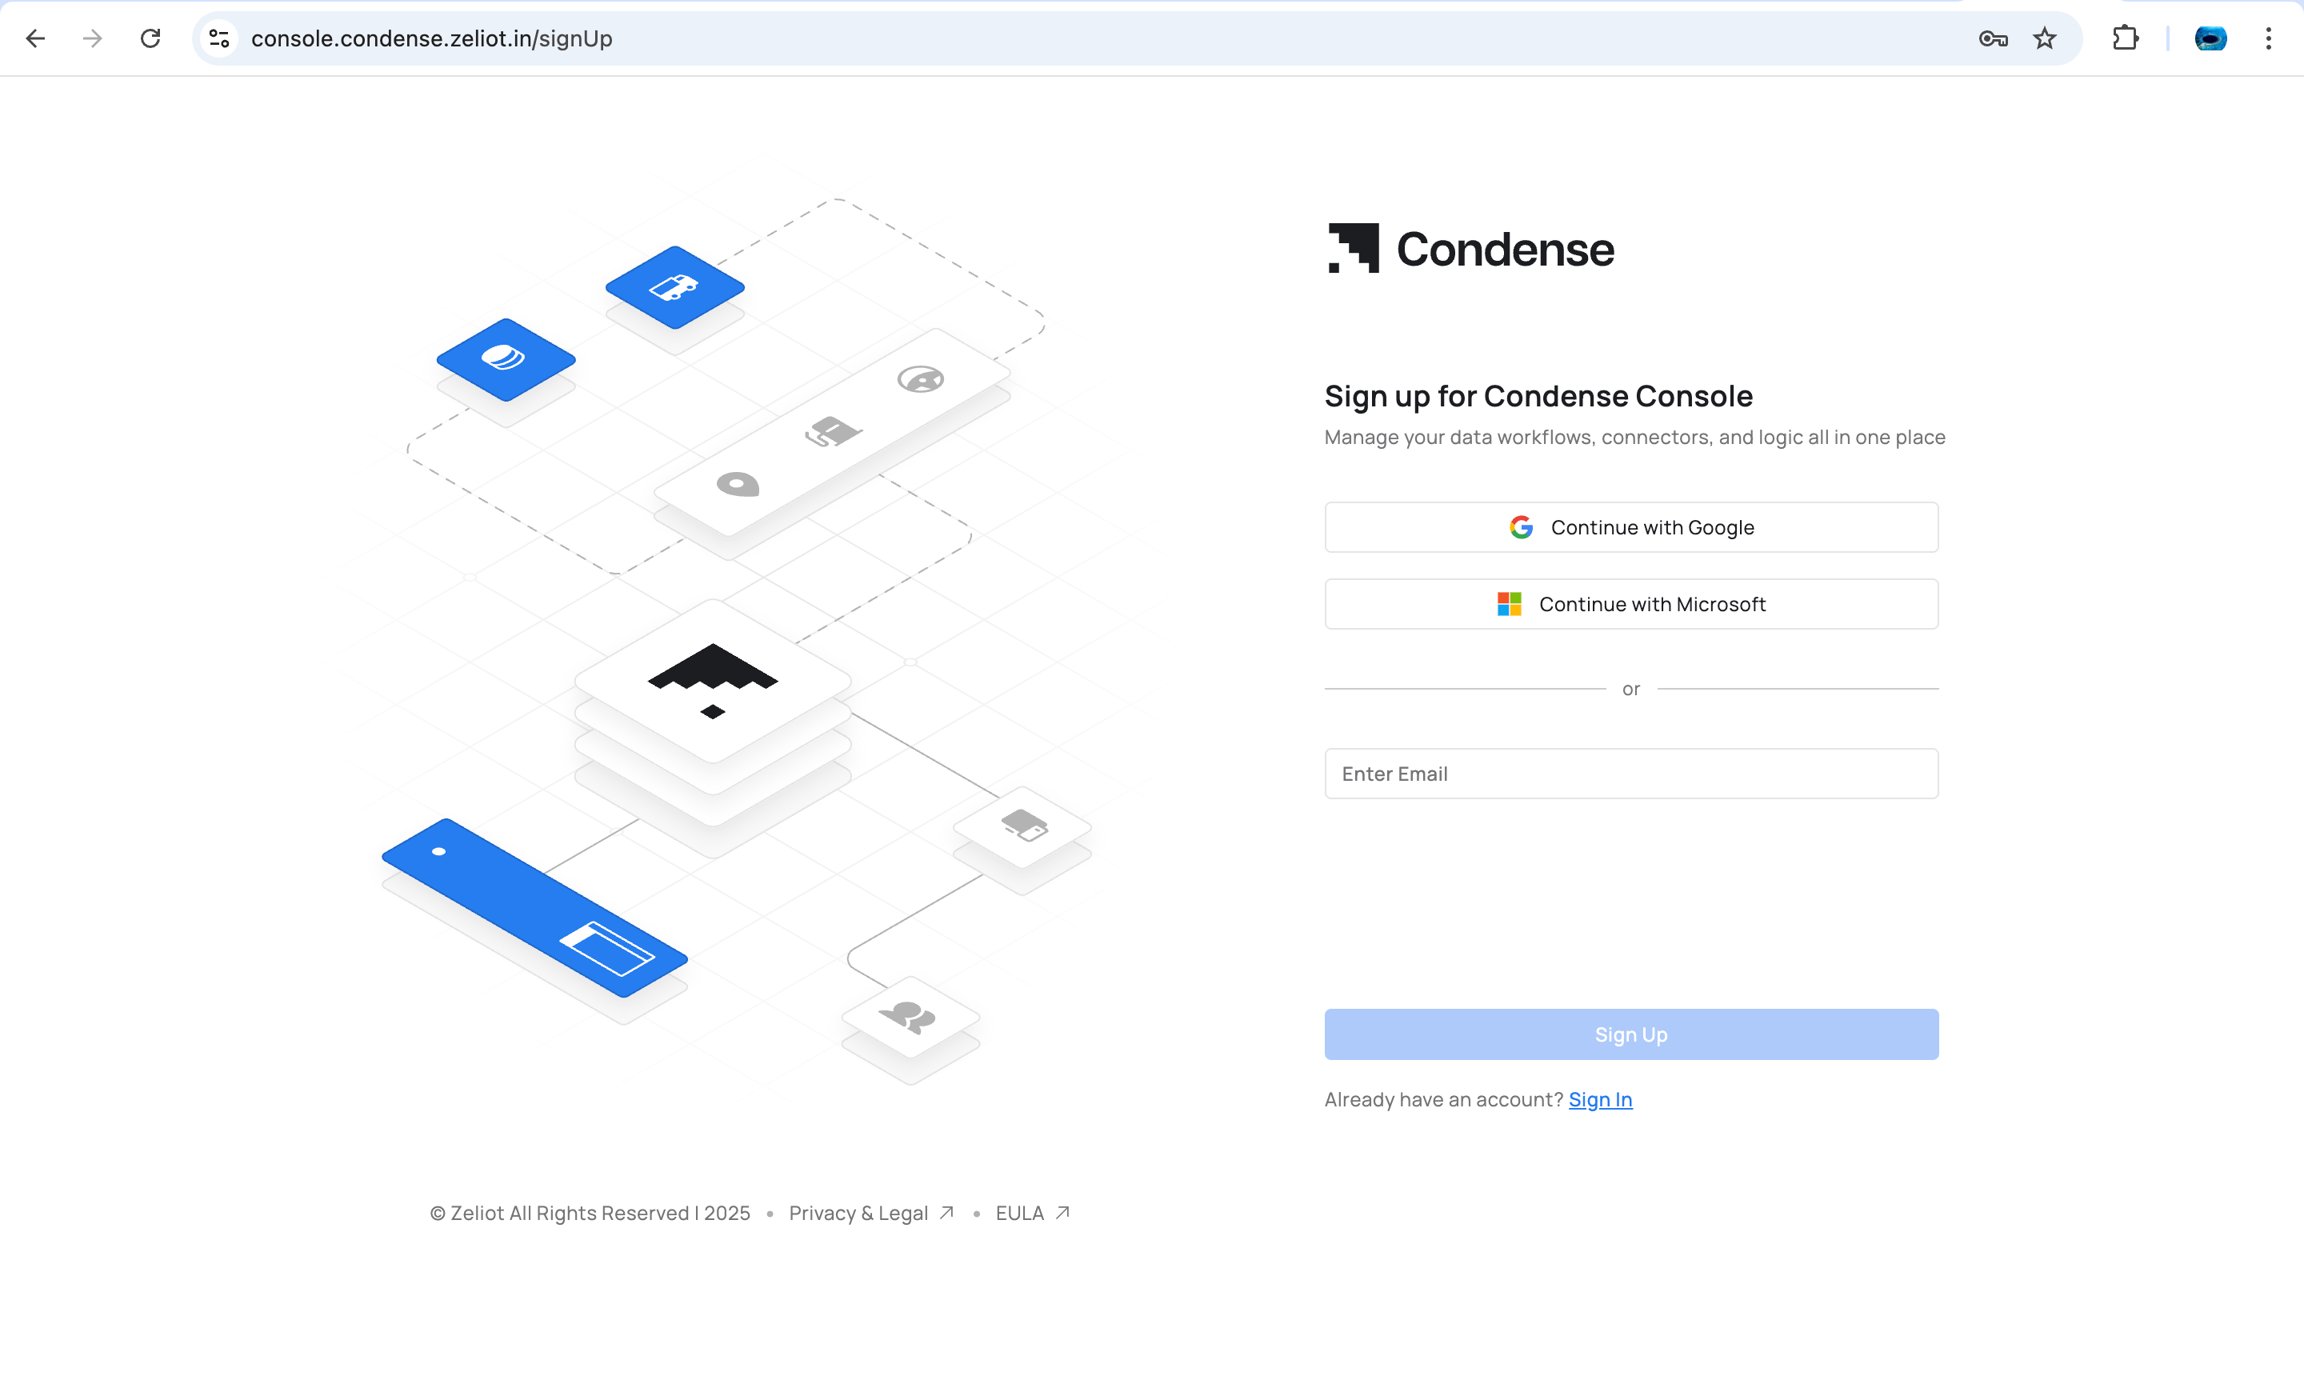
- The creator automatically becomes the Organization Admin
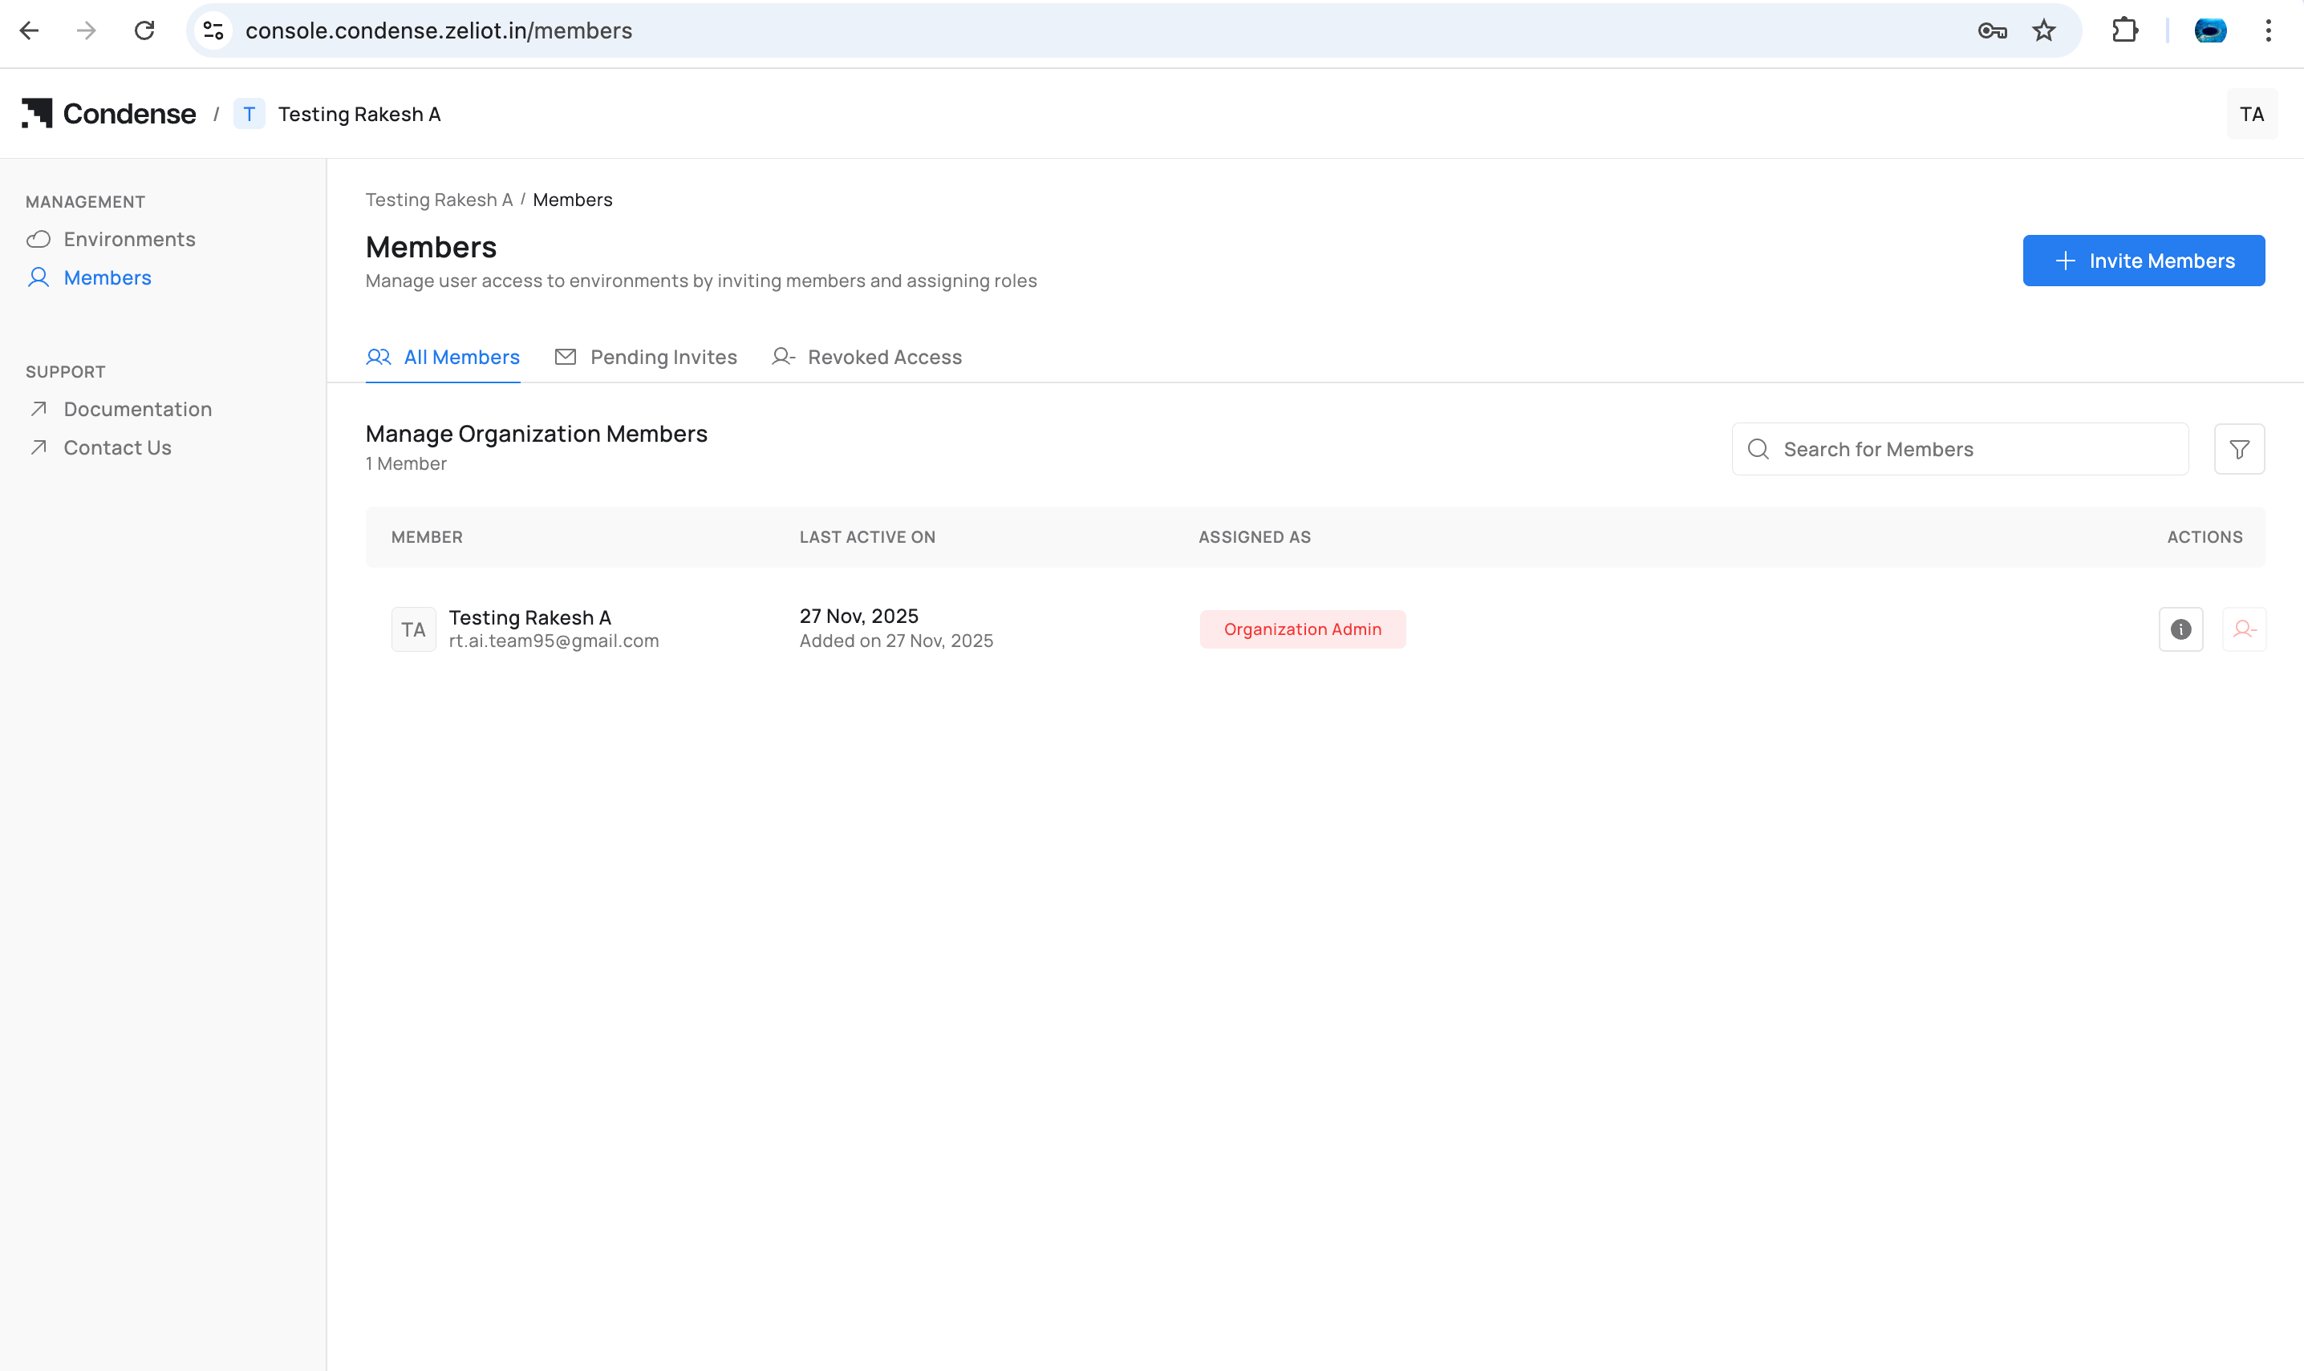
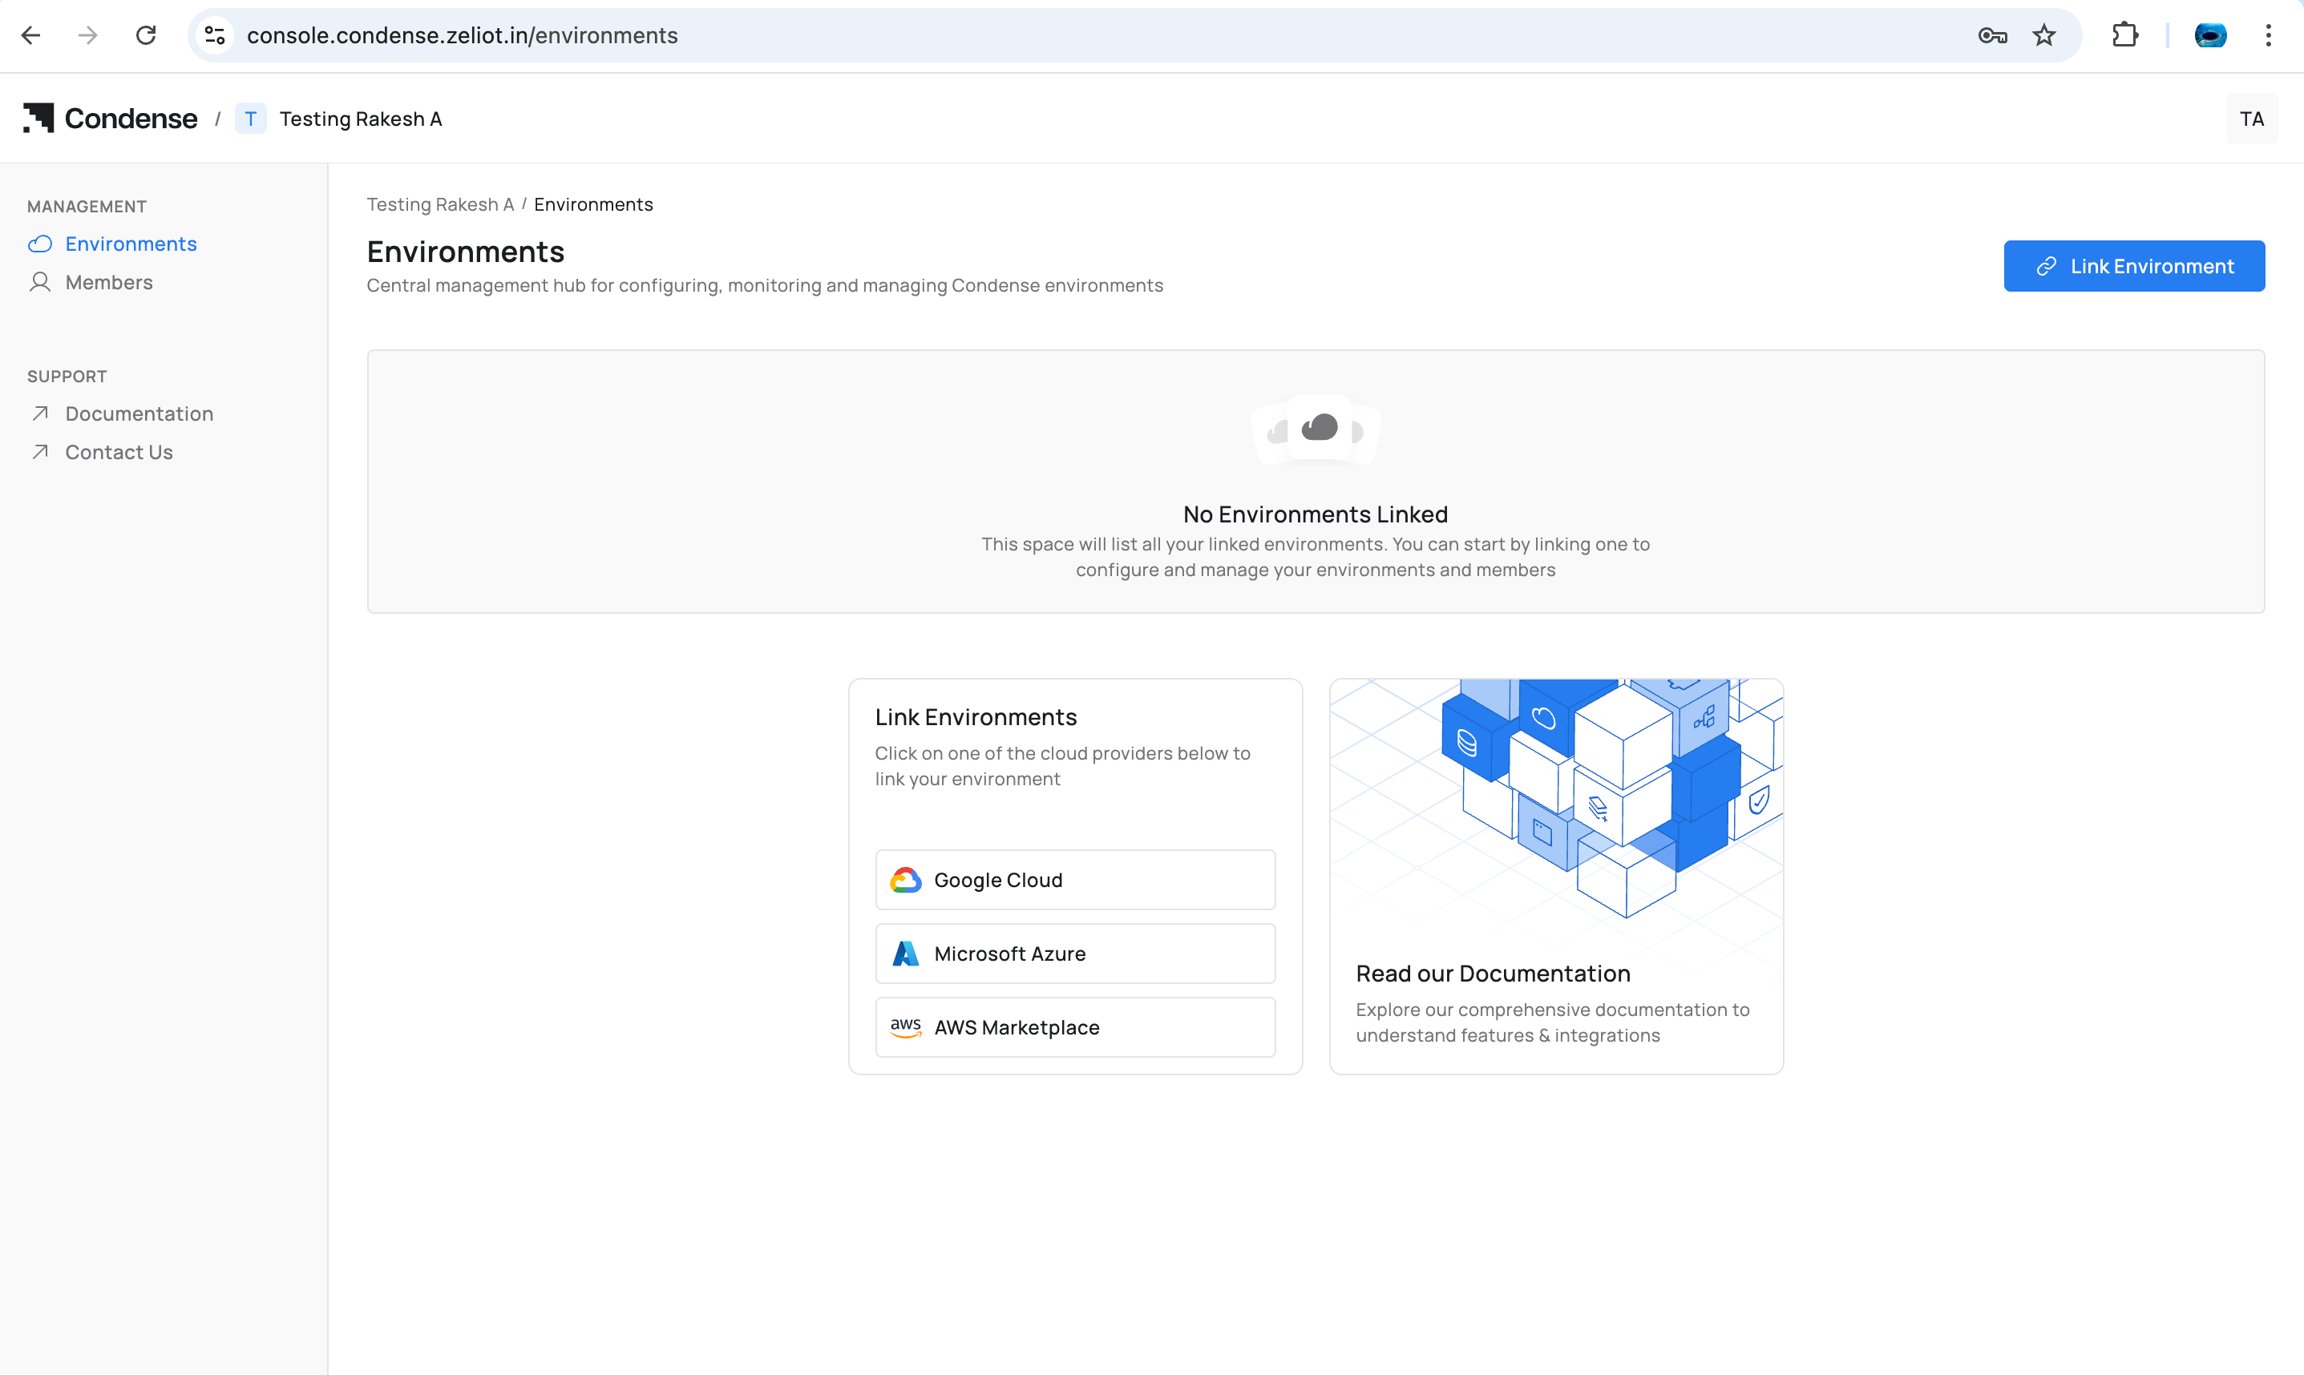
- Environment(s) can now be linked to the organization
Inviting Members
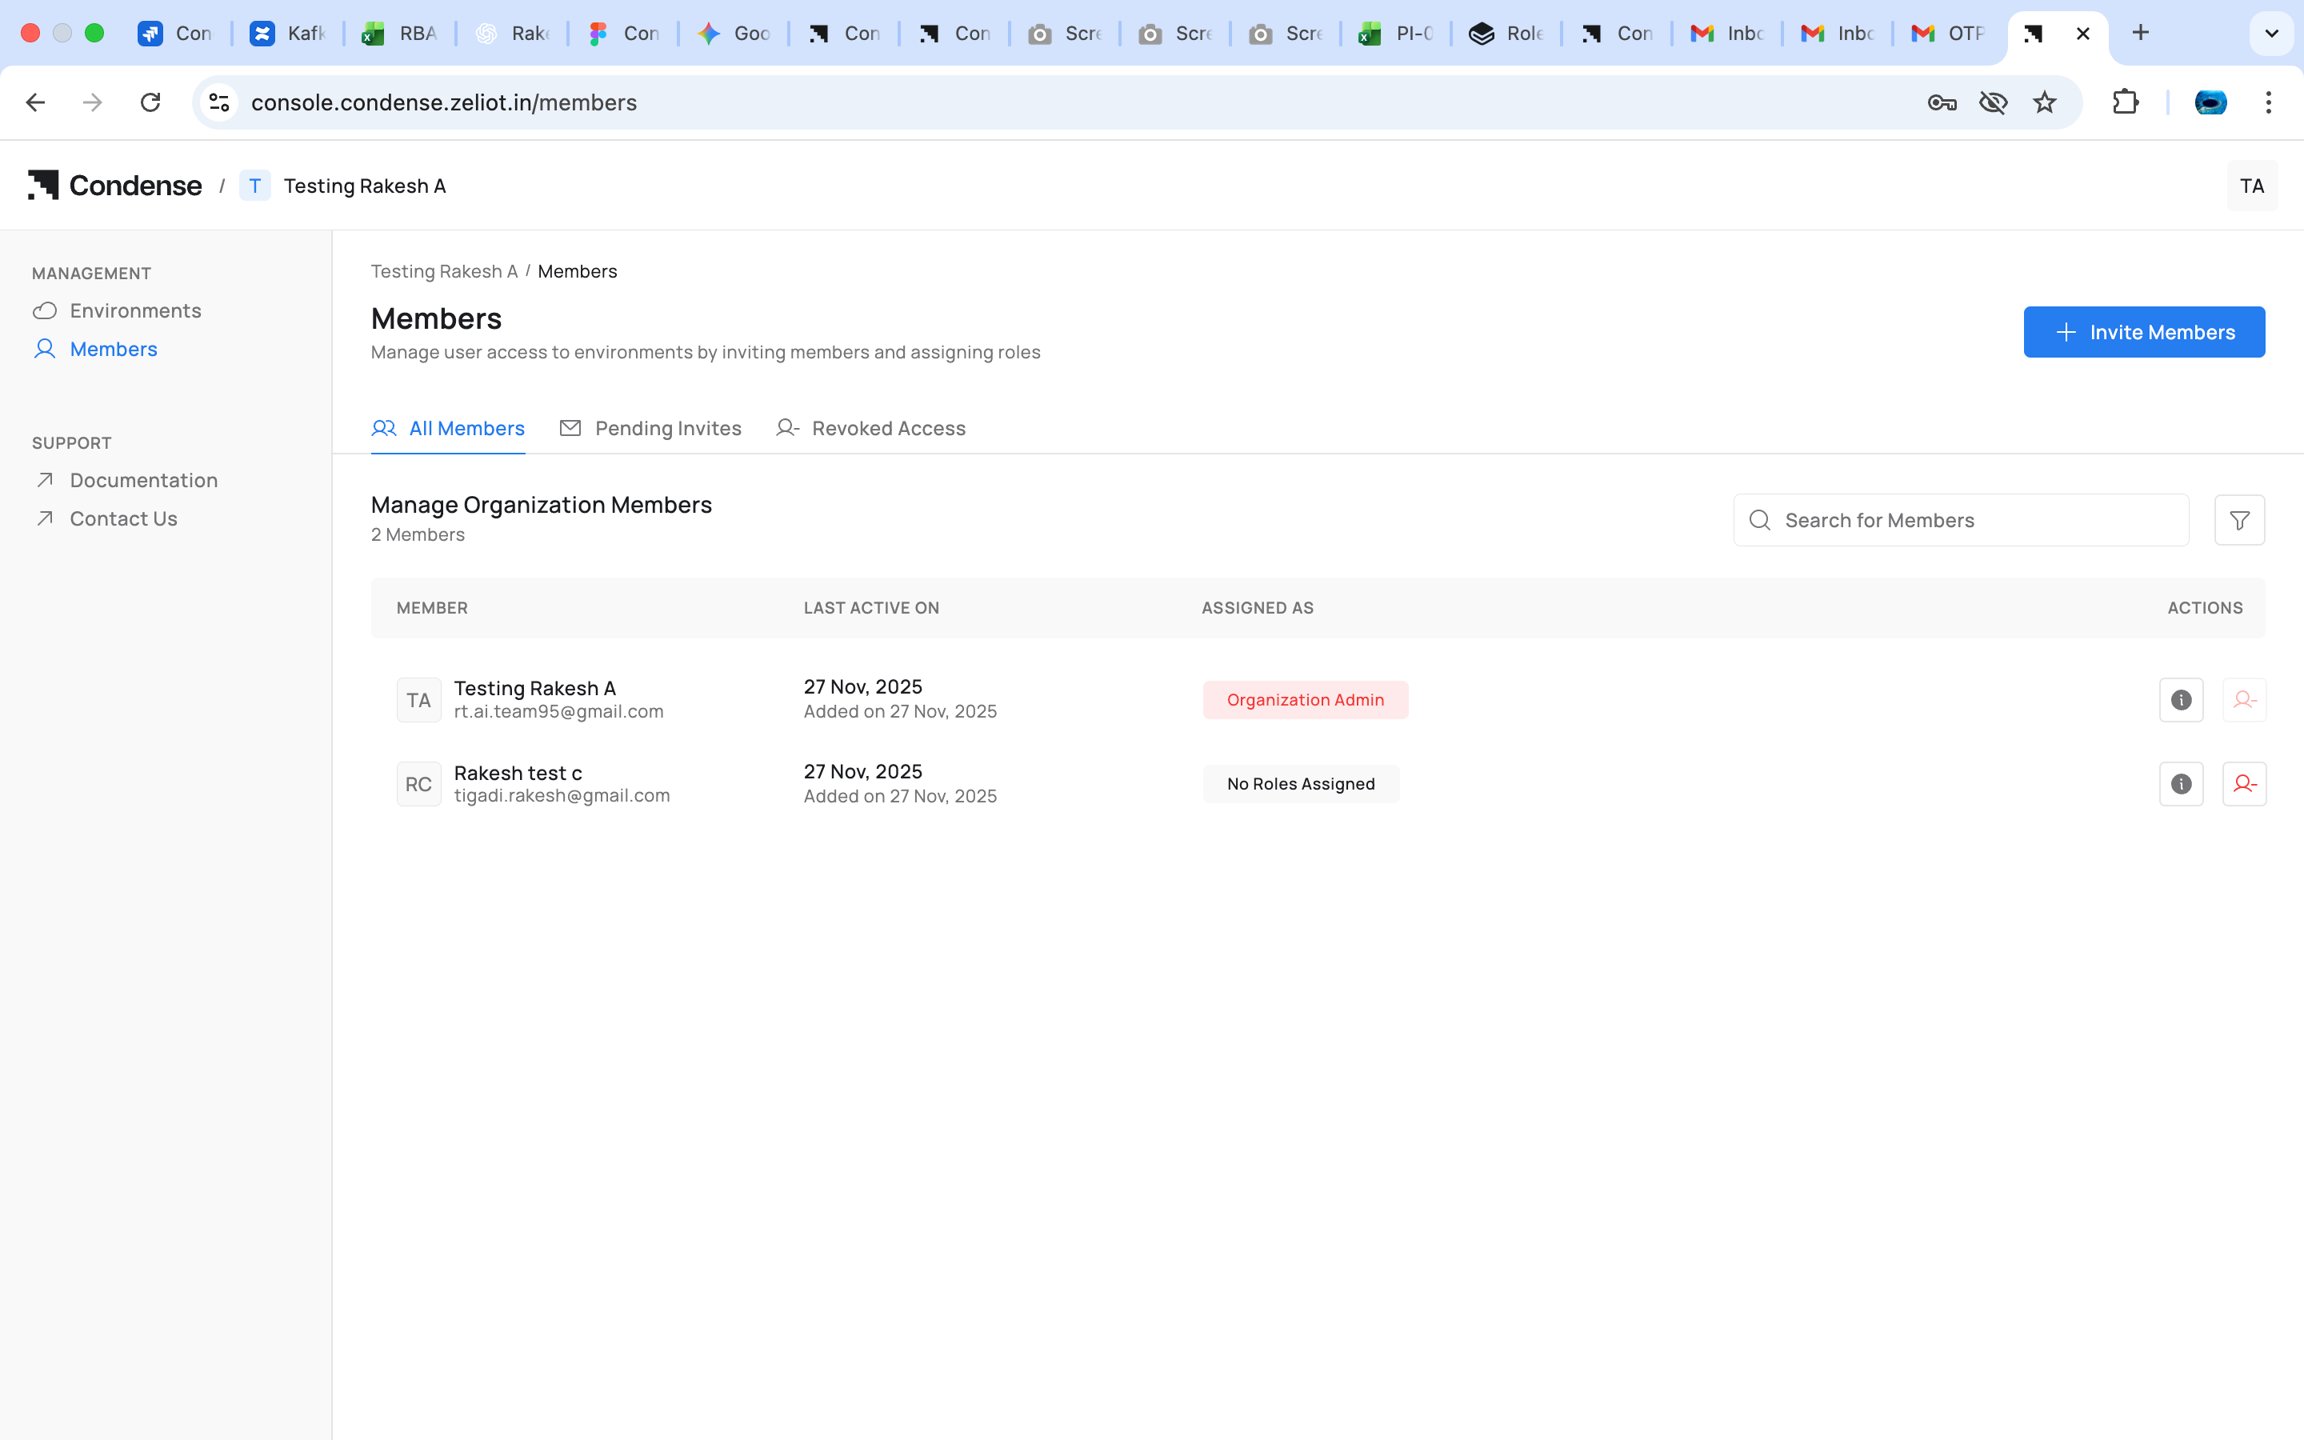
As Organization Admin:- Go to Members
- Select Invite Member
- Enter user details
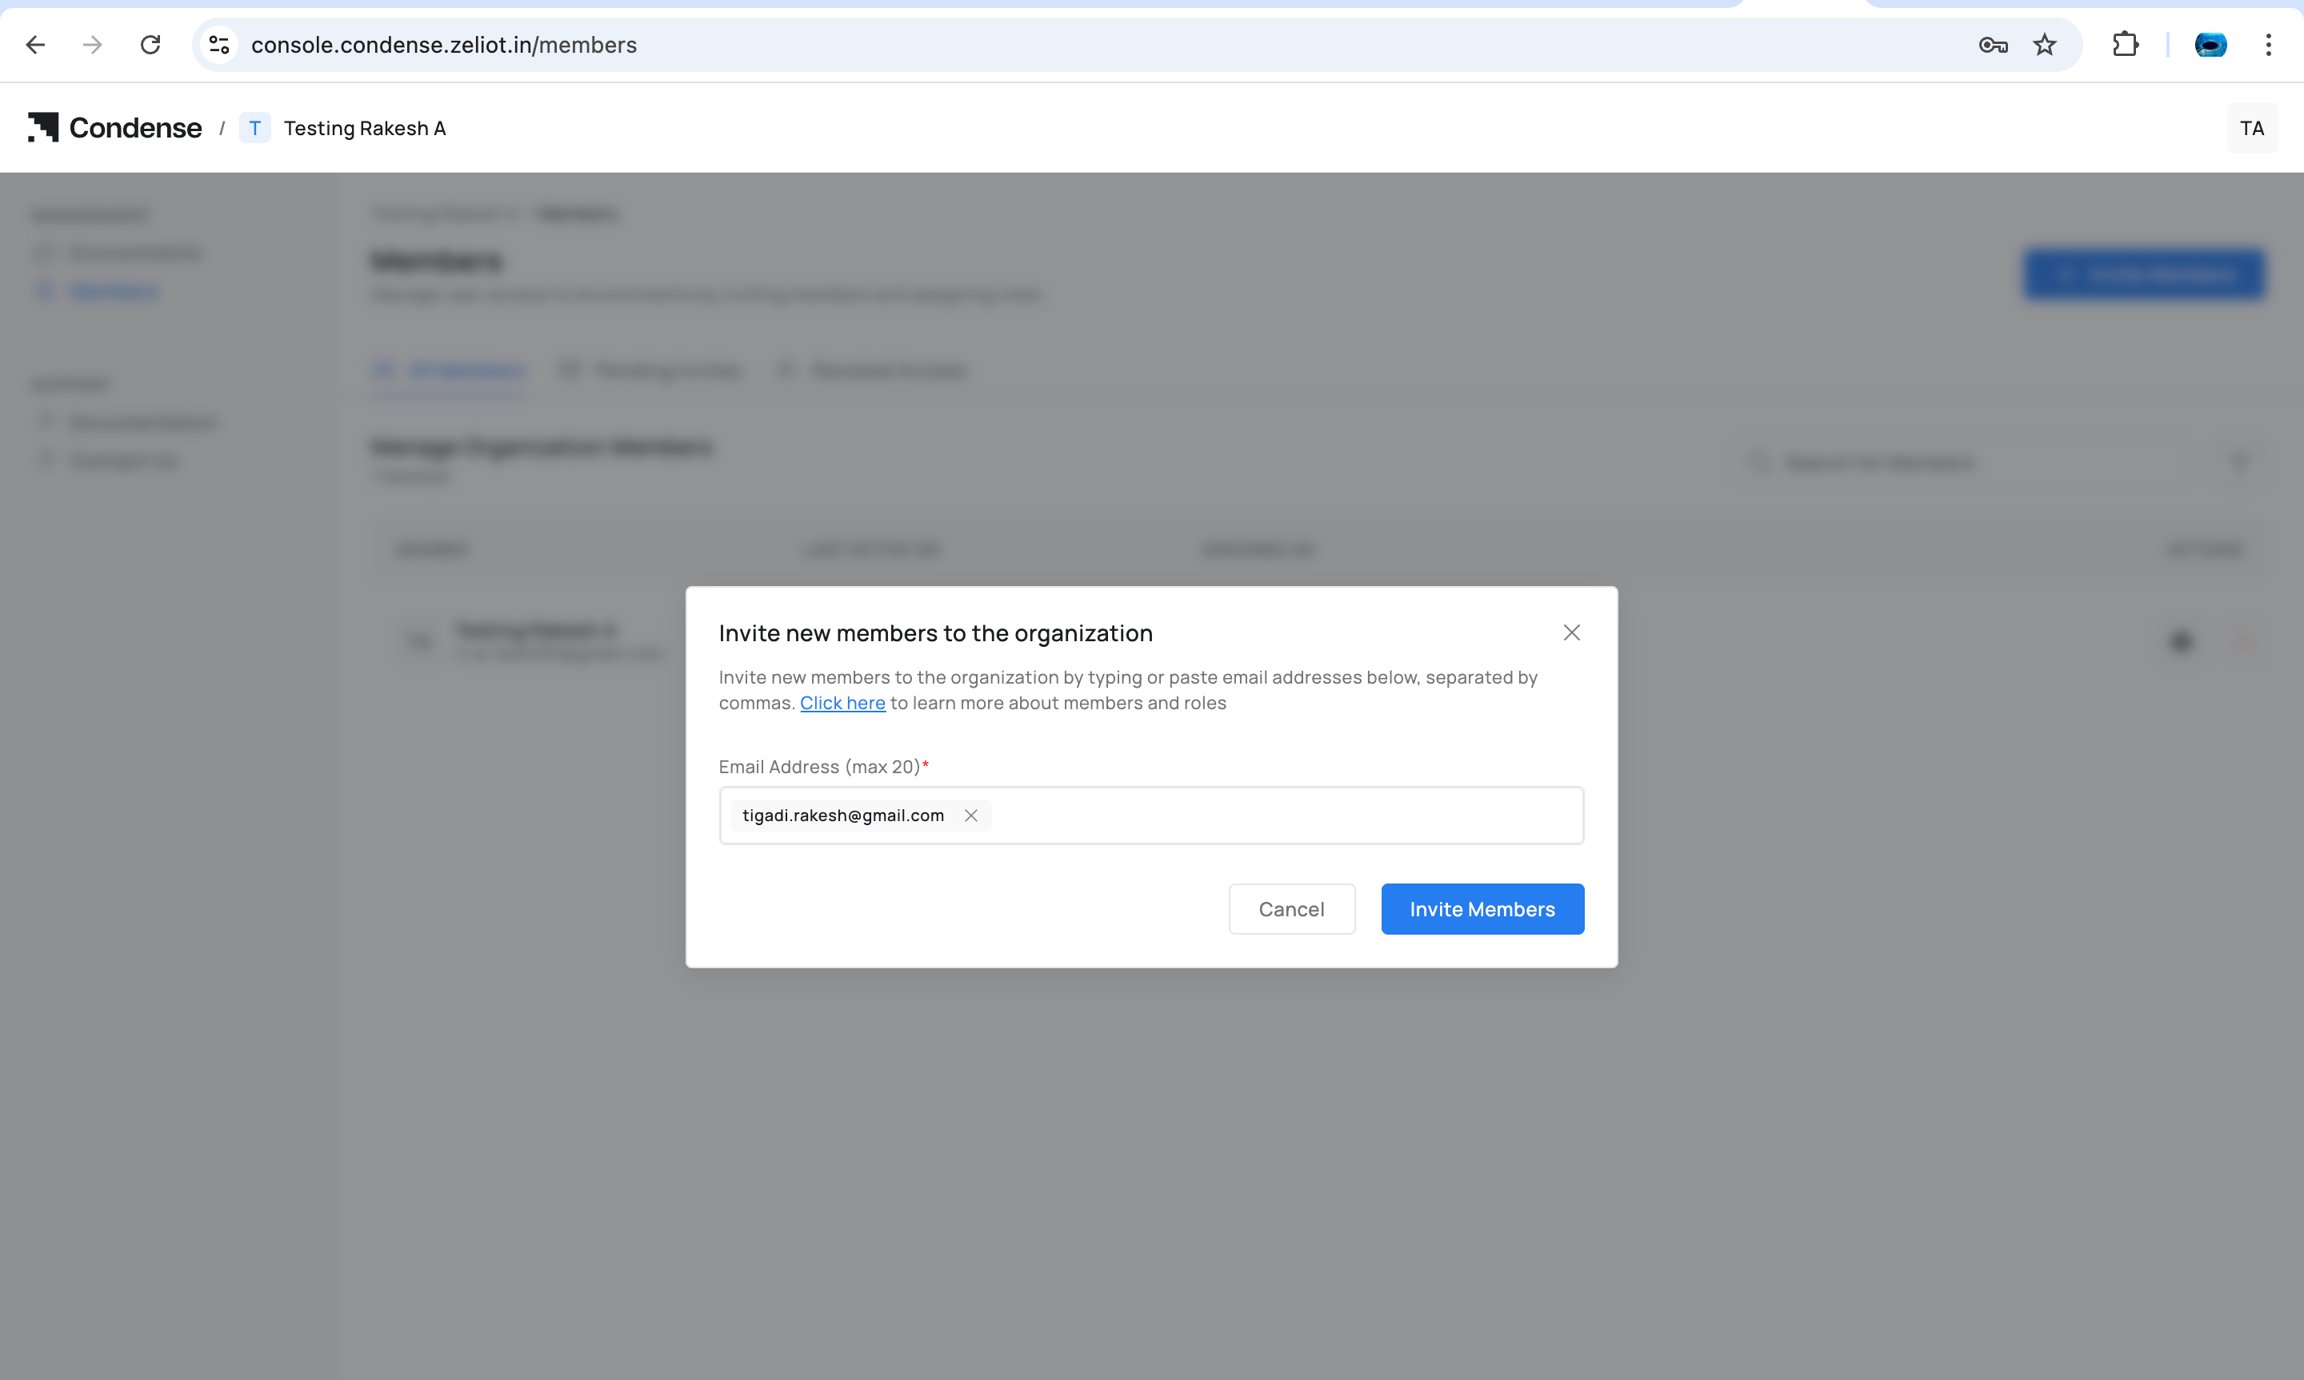
- Send invite
Inviting Existing Condense Users (New in v2.4.1)
Starting with Condense v2.4.1, users who already have a Condense account can be invited to additional organizations using the same email address. When the invitation is accepted:- No new Condense account is created.
- The new organization is added to the user’s existing account.
- Existing organizations remain unchanged.
- Roles and permissions are managed independently within each organization.
A single Condense account can belong to multiple organizations while maintaining separate members, environments, workspaces, and permissions for each organization.
- Select the member and assign one of the Organization-level roles:
- Organization Admin
- Account Admin
- Billing Admin
- Environment Admin (for selected environments)
- Environment User (for selected environments)
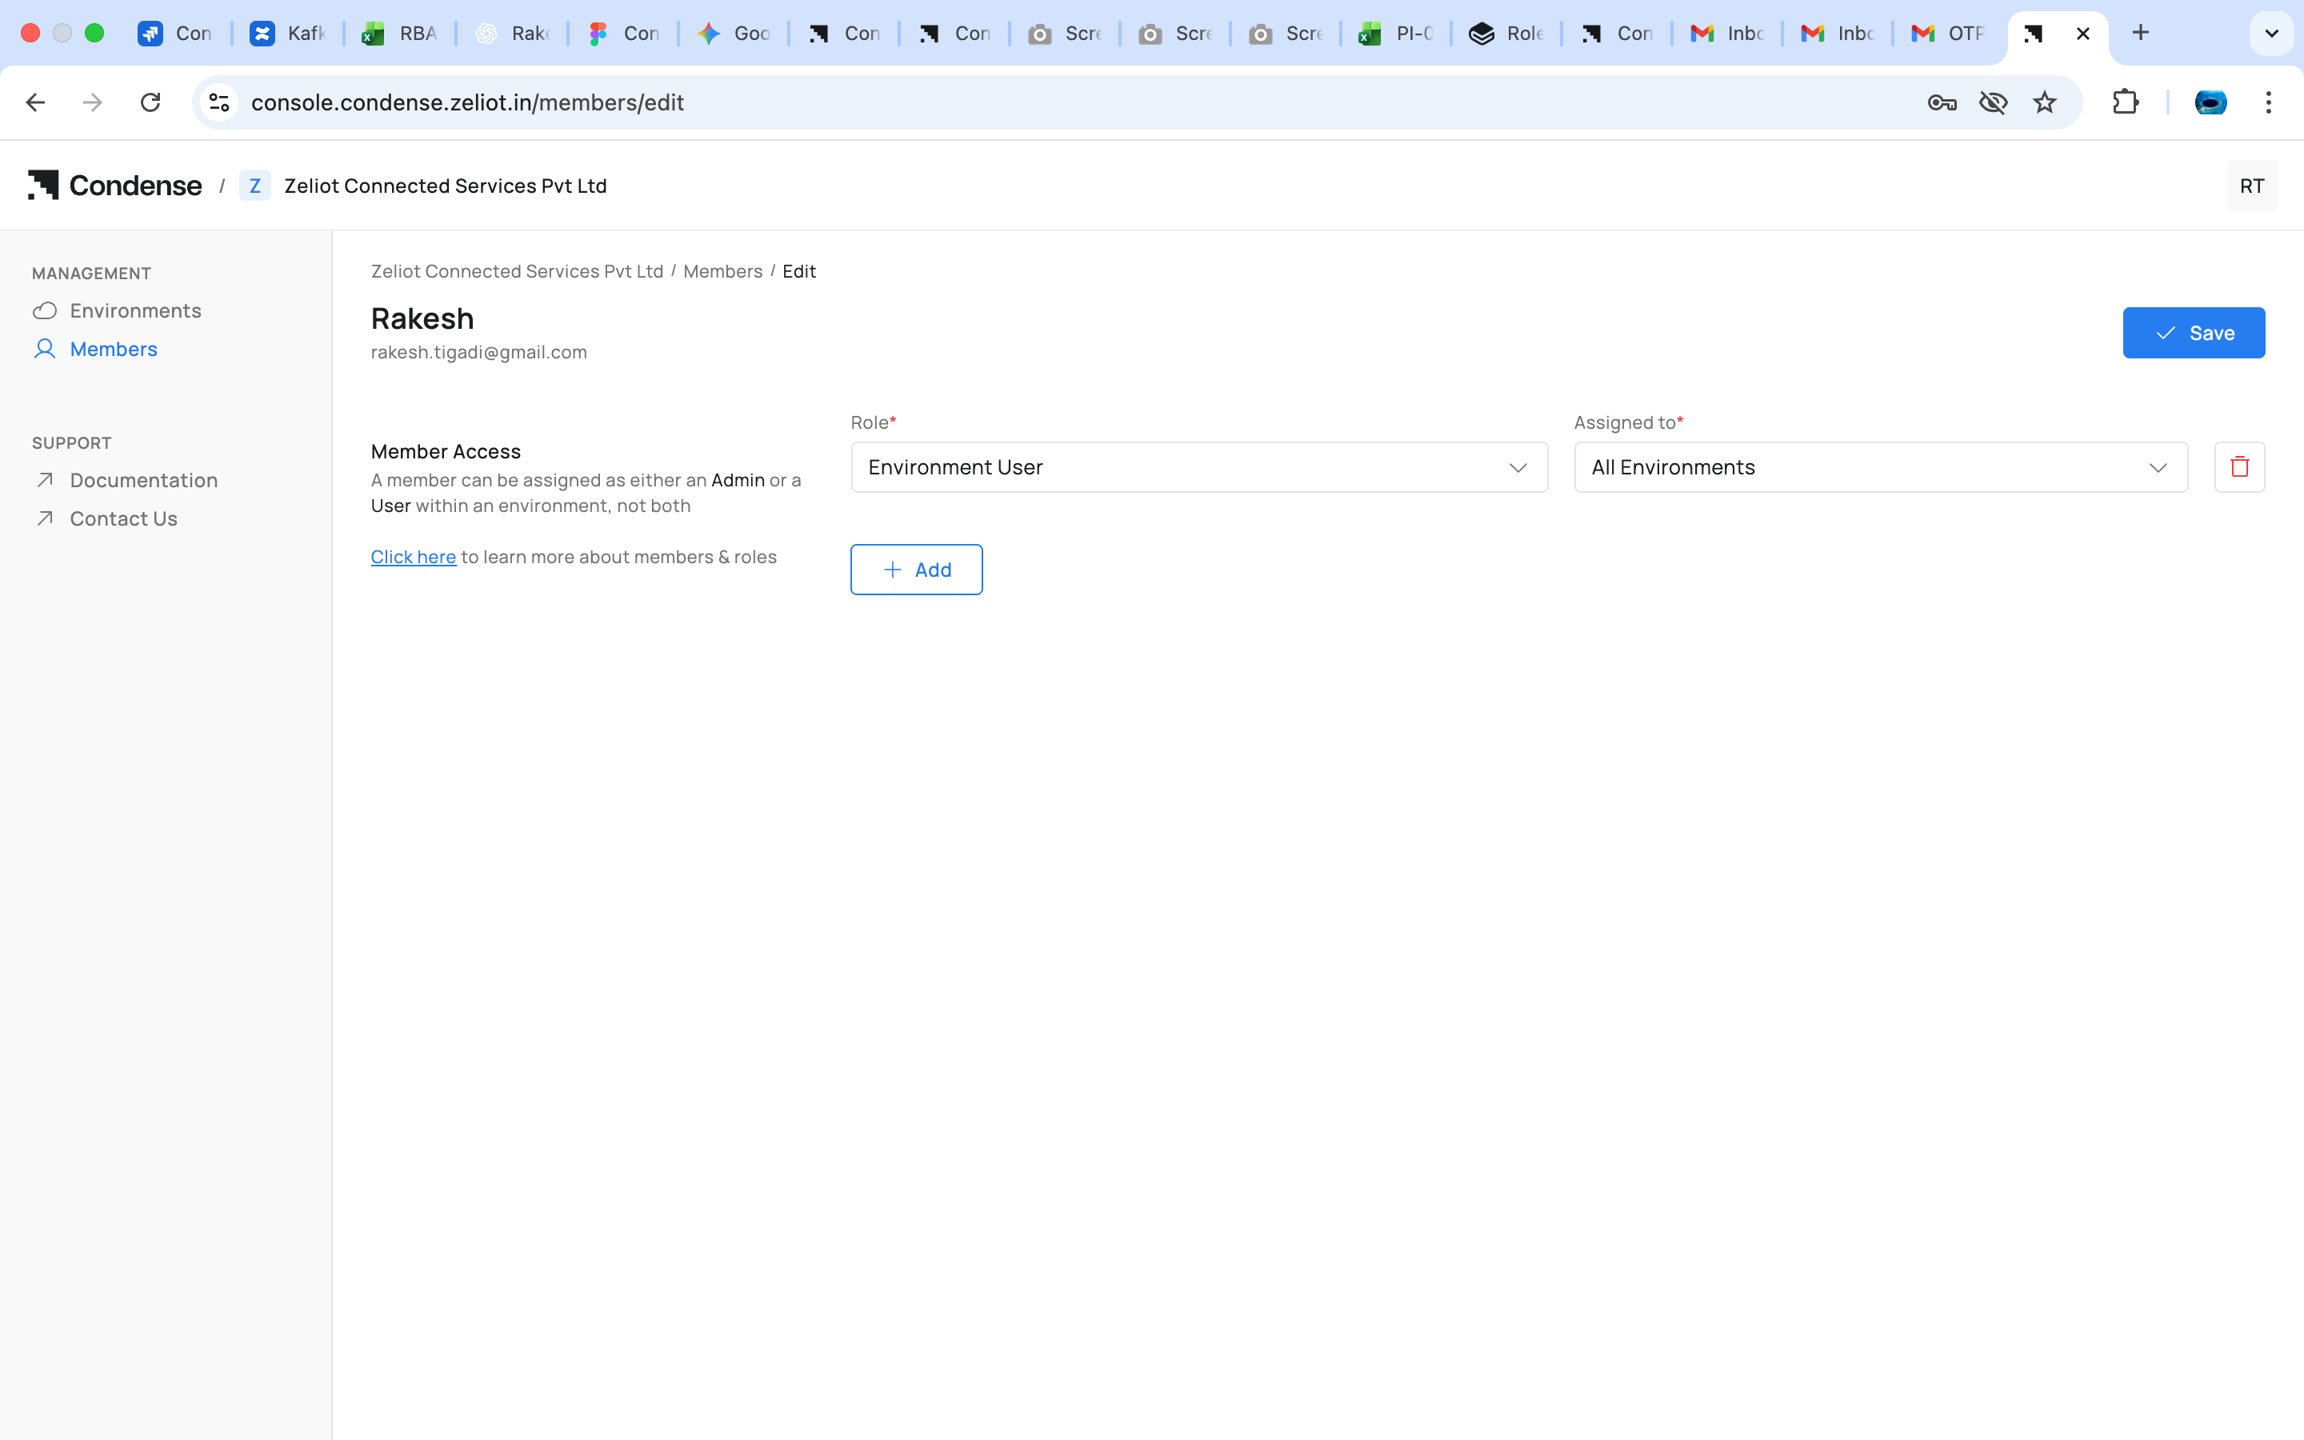
You cannot assign any role to member if there is no Environment is associated to organization
Assigning Organizational Roles
Organization Admins can assign:- Organization Admin
- Account Admin
- Billing Admin
Assigning Environment Roles
Organization Admin or Account Admin can:- Select a member
- Choose Add to Environment
- Select an environment
- Assign either:
- Environment Admin
- Environment User
Assigning Workspace Roles (inside Condense Core)
Only Environment Admins do this. For an Environment User:- Navigate to Members in Condense Core
- Select the Environment User
- Choose Assign Workspace Role
- Select role:
- Kafka Admin
- Maintainer
- Developer
- Viewer
- Select one or more workspaces
Note The role selected applies to all selected workspaces. Later additions must use the same role.
Example Scenario
Setup
Environments: Production, Testing Workspaces: FleetTracking, ColdChain, SandboxTeam
User Experience
- Anita Full authority across both environments and all workspaces.
- Bharat Sees Production only. Sees only FleetTracking because of the Kafka Admin role.
- Divya Sees all workspaces in Testing. Can deploy and manage connectors in Sandbox.
- Eshan Sees Production. Sees FleetTracking and ColdChain as Developer.
- Farah Sees Sandbox with read-only access.
Behavior
- Environment Admins see and operate across all workspaces of their environments
- Environment Users only see the workspaces they have a role for
- Workspace roles for an Environment User always remain uniform across all selected workspaces
Capability Overview
Condense RBAC provides a structured, predictable access model across three layers:
- Organization Layer : governs who administers the organization and who can assign access
- Environment Layer : determines seniority and visibility for operations
- Workspace Layer : controls fine-grained operational capabilities
Lifecycle Guide
Lifecycle Guide
The following lifecycle illustrates how a user is onboarded into an organization and granted access to Condense resources.1. Create an Organization
A new user signs up for Condense and creates an organization. The creator is automatically assigned the Organization Admin role. Outcome:- Organization created
- Organization Admin assigned
- Ready to link environments
2. Link an Environment
The Organization Admin links one or more Condense environments to the organization. Outcome:- Environment becomes available for member assignment
- Environment roles can now be configured
3. Invite Members
The Organization Admin invites users by entering their email address and sending an invitation. Users receive an invitation email and join the organization after accepting the invitation. Outcome:- Member added to the organization
- Ready for role assignment
4. Assign Organization Roles
Assign one of the available organization-level roles based on administrative responsibilities. Available roles include:- Organization Admin
- Account Admin
- Billing Admin
- Administrative permissions configured
5. Assign Environment Roles
Assign users to one or more linked environments. Available roles include:- Environment Admin
- Environment User
- User gains access to the selected environments
6. Assign Workspace Roles
For Environment Users, assign workspace-level permissions within Condense Core. Available workspace roles include:- Kafka Admin
- Maintainer
- Developer
- Viewer
- User receives access to the required workspaces
7. Start Working
Once all required roles have been assigned, members can:- Access their assigned environments
- Open authorized workspaces
- Build and deploy pipelines
- Manage connectors and transforms (based on role)
- Monitor Kafka resources and applications
8. Ongoing Administration
Organization Admins can continue to manage the organization by:- Inviting new members
- Updating member roles
- Removing members
- Linking additional environments
- Managing organization settings
Frequently Asked Questions (FAQs)
Frequently Asked Questions (FAQs)
Q1: Who can invite members to an organization?
Only users with the Organization Admin role can invite new members to an organization and assign organization-level roles.Q2: What happens after a member accepts an invitation?
Once the invitation is accepted, the member is added to the organization. An Organization Admin can then assign the appropriate organization and environment roles based on the user’s responsibilities.Q3: Can I invite someone who already has a Condense account?
Yes. Starting with Condense v2.4.1, existing Condense users can be invited to additional organizations using the same email address. The new organization is added to their existing account without requiring a new registration.Q4: Can a user belong to multiple organizations?
Yes. A single Condense account can belong to multiple organizations. Users can switch between organizations while maintaining separate roles, permissions, environments, and workspaces for each organization.Q5: Do I need a different email address for each organization?
No. The same email address can be used across multiple organizations. Each organization manages access independently.Q6: Can I assign roles before linking an environment?
Organization-level roles can be assigned without an environment. However, Environment Admin and Environment User roles can only be assigned after at least one environment has been linked to the organization.Q7: What is the difference between Organization, Environment, and Workspace roles?
- Organization Roles control administrative access to the Condense Console.
- Environment Roles determine access to specific Condense environments.
- Workspace Roles provide fine-grained permissions within individual workspaces in Condense Core.